
Solutions
Everyday credential work without replacing your security stack
VaultPilot handles shared credentials, selected-record sharing, Discovery findings, recovery, and directory metadata on your own server. PAM session brokering, SIEM, and vulnerability scanning stay with other tools.
Shared credentials under global and vault roles
Personal and shared vaults hold passwords, credentials, API keys, secure notes, certificates, and files. Global roles and vault roles keep administration apart from day-to-day use. Ownership of the source systems stays outside the vault; VaultPilot rotates only Active Directory credential records, through a connected DC Agent.
- Tags, URLs, and vault placement on every record
- Viewer, Editor, and Manager vault roles
- Owner, Admin, Auditor, and User global roles
Share a few records without exporting the vault
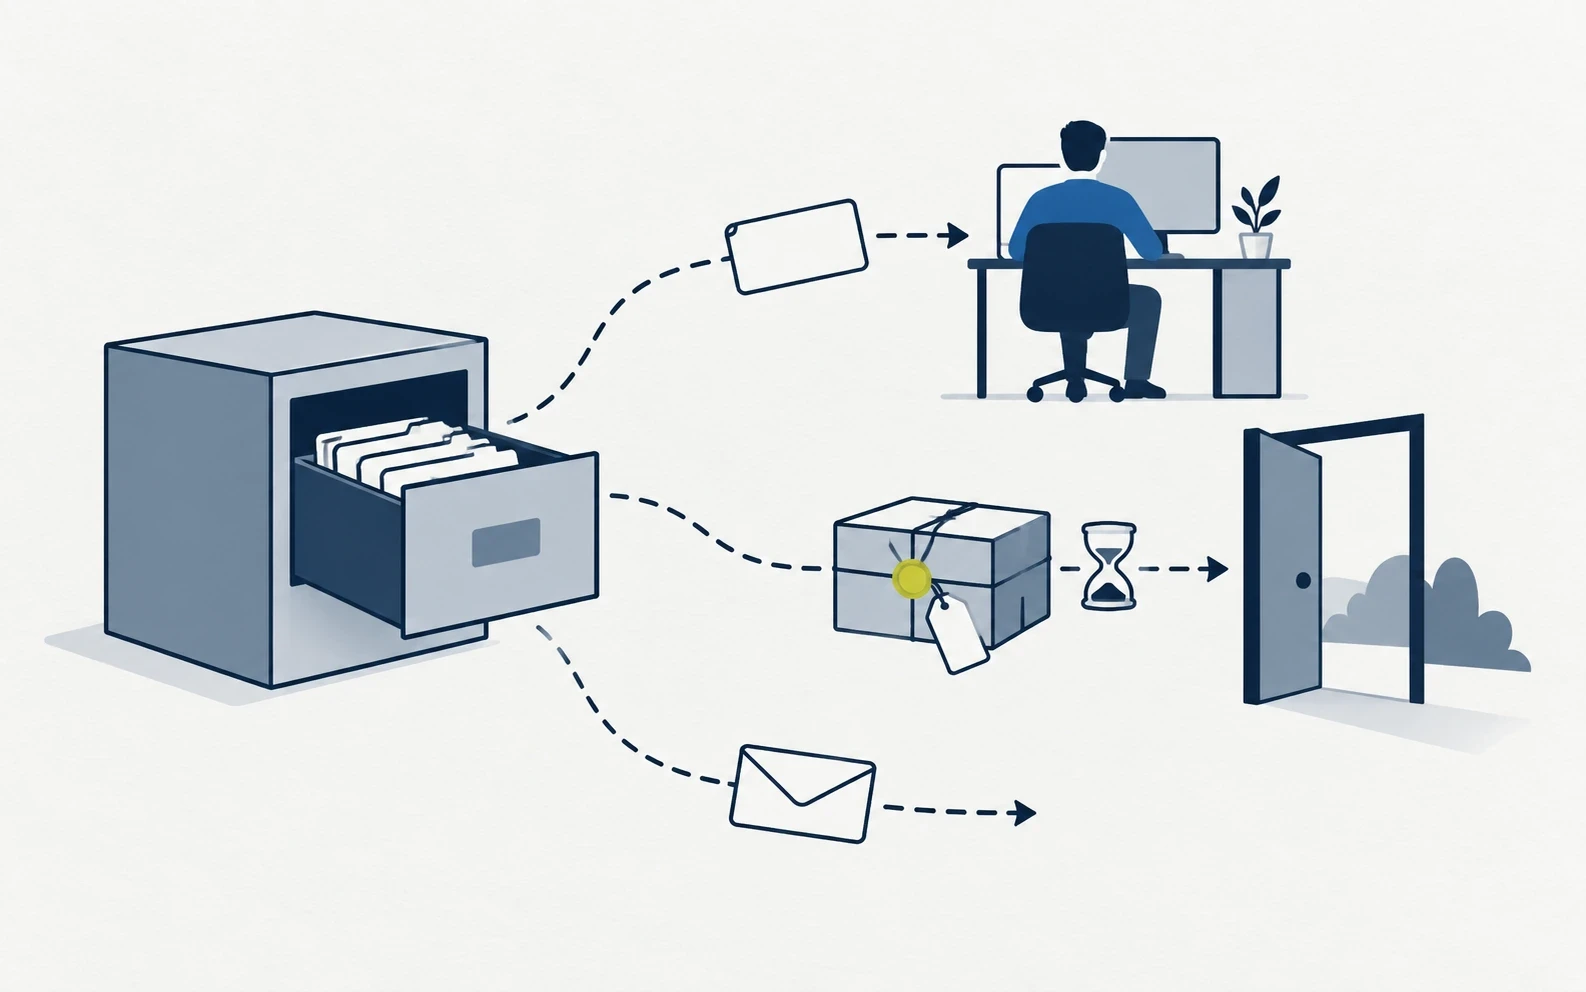
Internal sharing wraps the selected records for a registered VaultPilot user. External sharing puts selected records in a passphrase-protected package that is decrypted in a local browser and stops opening after its expiry date or open limit. The passphrase travels through a separate channel.
- A check that the recipient’s public key is ready
- Eligible files can be included in an external package
Exposure signals, recovery readiness, and directory context
Discovery reads private-network surfaces, TLS signals, and approved files without changing anything. Recovery keeps Quick Recovery and the full server backup apart. The optional DC Agent syncs directory metadata and health. VaultPilot has no SSO, SCIM, or automatic provisioning.
- Discovery findings reviewed by a person
- Quick Recovery leaves out file records, audit history, and server settings
- The AD bind password is not sent to VaultPilot
- No brute force, automatic remediation, or session brokering
See VaultPilot in your own environment
Tell us what the evaluation should cover, or open the live demo with sample data first.