
Encrypted sharing: send selected records inside or outside the team
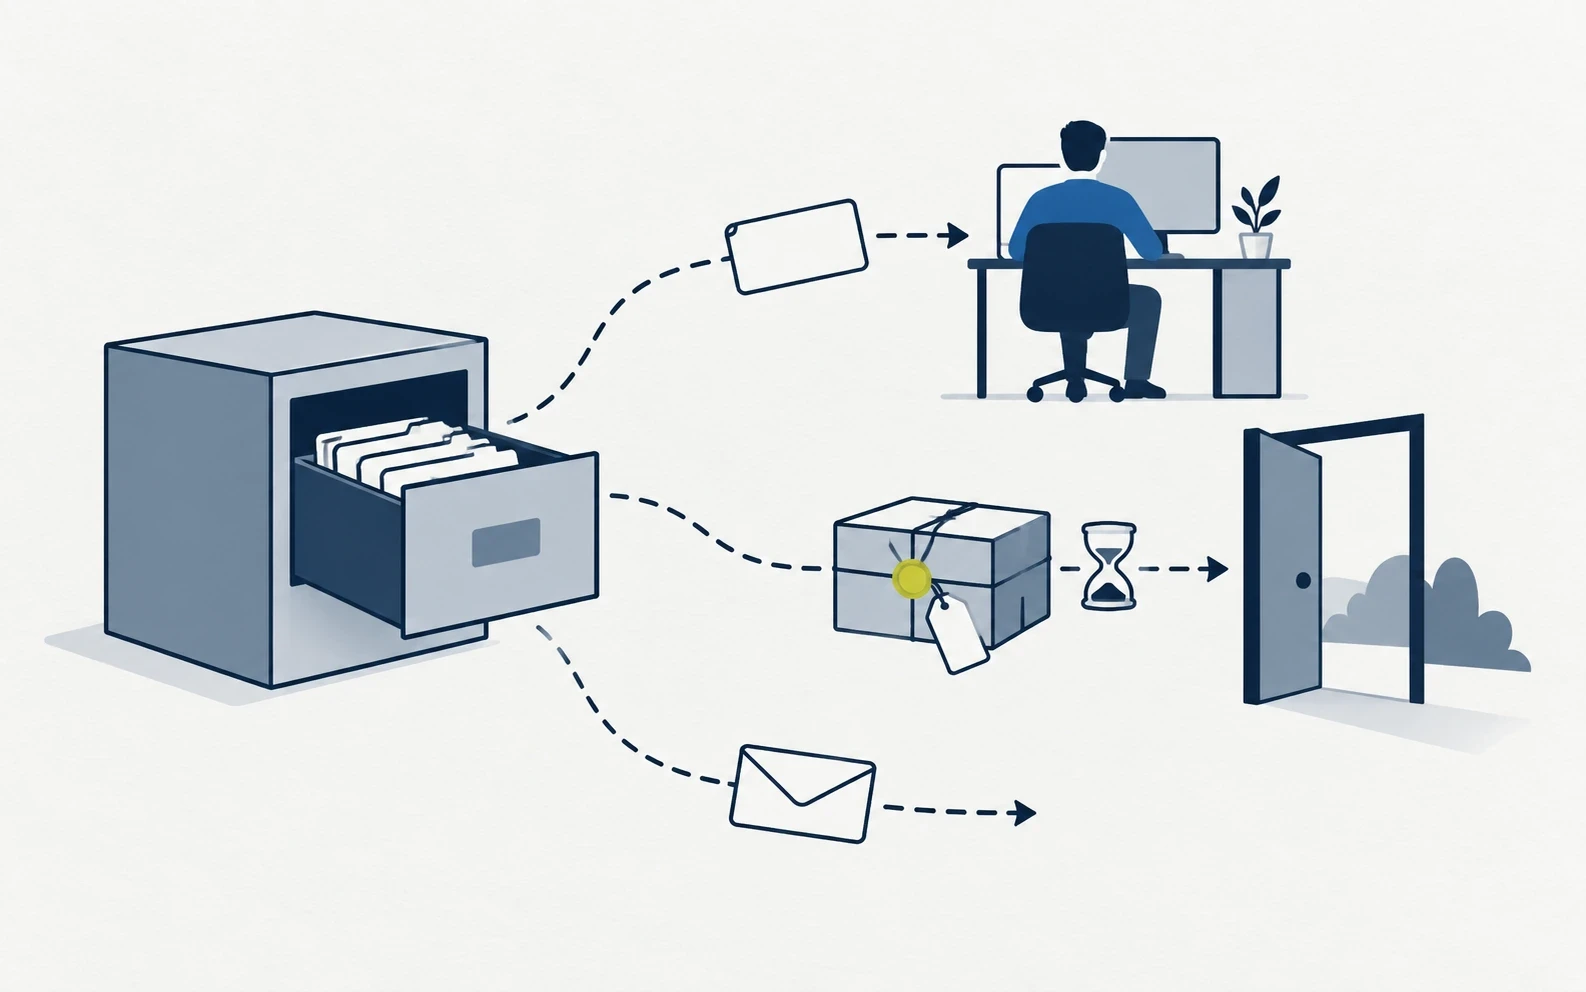
VaultPilot shares in two ways: an encrypted bundle for registered internal users, and a passphrase-protected package for people outside the server. Either way, you pick the records and the recipient. You can revoke only an internal share later; once you send an external package, you cannot take it back centrally.
- What travels
- Selected records only
- External open
- Local browser decrypter
- Controls
- Expiry, open limit, internal revoke
Internal recipients open shares with their own account
For an internal recipient, VaultPilot checks the account and its public key, and the browser encrypts the selected records for that person. The recipient saves copies of those records into their own vault and never gets the whole source vault. Creation, acceptance, and revocation each leave an audit event.
External recipients get an encrypted package
A recipient outside the server opens the package with the local HTML decrypter, entirely in the browser. Send the package through one channel and the passphrase through another. For a one-time handoff, keep the open count low.
After the package leaves your hands
The result screen shows the package, the passphrase, and delivery guidance, and it offers the decrypter ZIP for download. VaultPilot keeps no server copy or history row for an external package. The open limit is a local counter in the recipient's browser. On the recipient side, the decrypter reports each failure as its own error.
Limits to know
- Revoking an internal share blocks future opens, but it does not delete copies the recipient already saved or take back what they viewed.
- A package sent to the wrong person stays openable until it expires or runs out of opens. Change every secret inside it through that secret's own procedure.
- Never put the package or its passphrase in a support request.
Step-by-step checks
Read more in the guides: Sharing and offline decrypter, Sharing screen guide, External sharing troubleshooting
See VaultPilot in your own environment
Tell us what the evaluation should cover, or open the live demo with sample data first.