
Zero knowledge: the vault unlocks in the browser session
As a zero-knowledge encryption password manager, VaultPilot encrypts vault data in the browser before the server stores it. The server authenticates requests and keeps encrypted payloads, wrapped keys, salts, and operational metadata. Unlocked vault keys exist only in the browser's session memory.
- Master password
- Processed in the browser
- Vault unlock
- Session memory
- Server storage
- Ciphertext and metadata
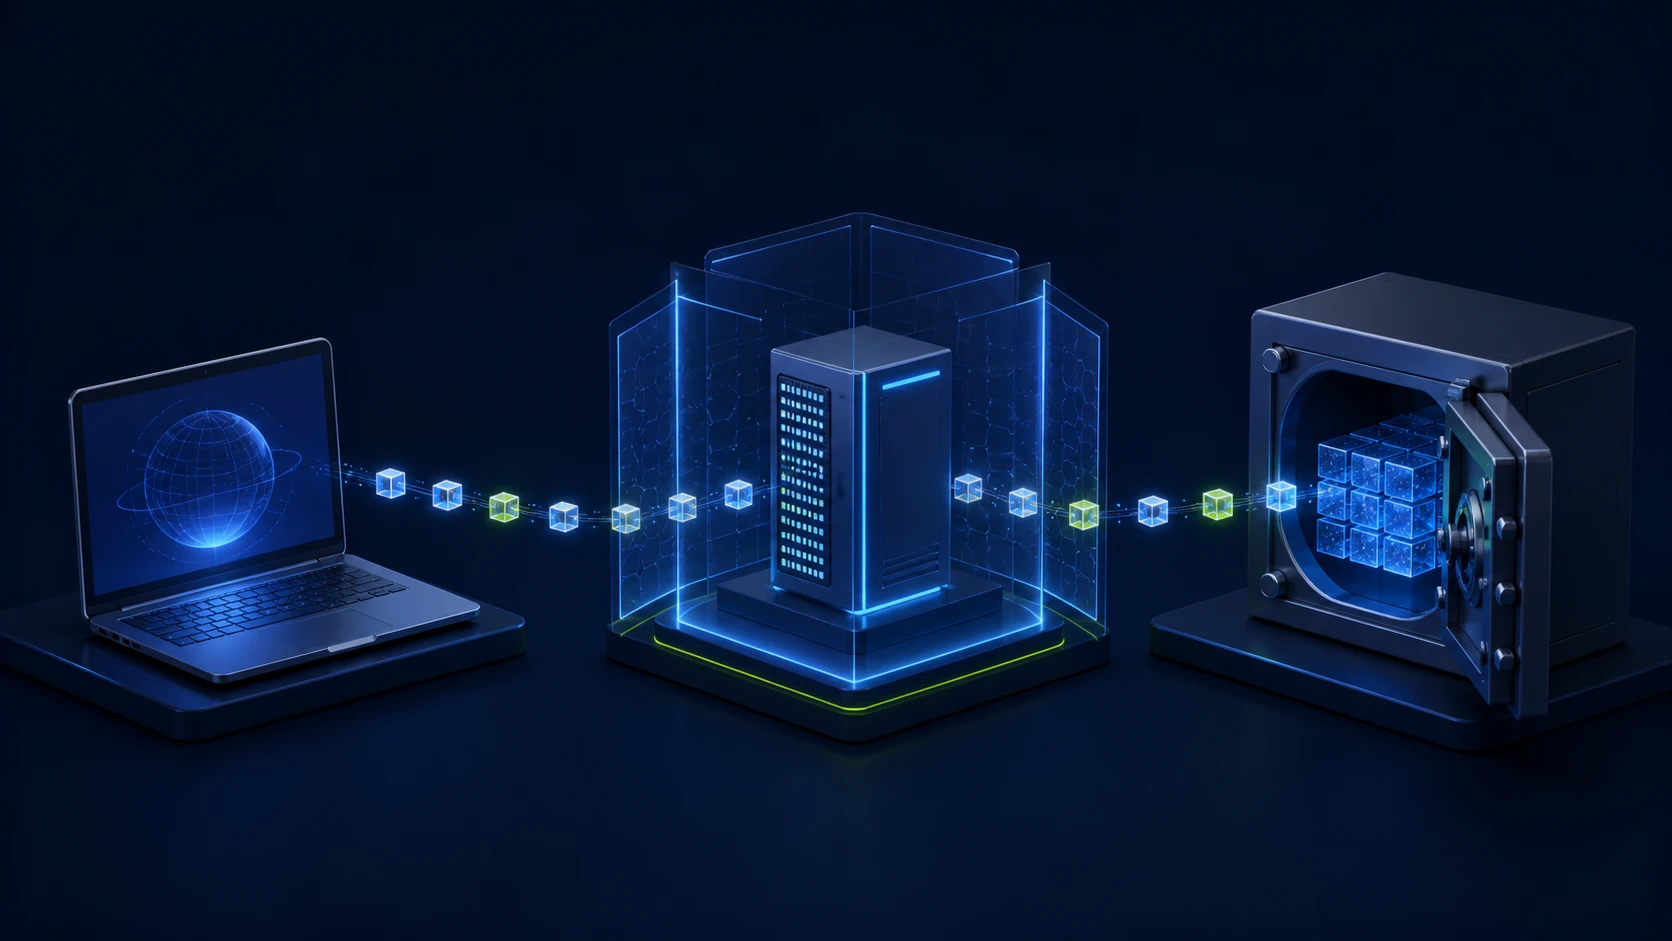
Signing in does not unlock the vault
A server session decides who may use the server, and it reveals no vault plaintext. The material that unlocks the vault keys is derived from your master password in the browser, and it opens only the keys you are authorized to use.
- The master password is not sent to the server
- Role and vault access still apply
What the server keeps
The browser encrypts supported secret values before the server saves them. The local SQLite database holds what the product needs to run:
- Encrypted secret payloads
- Wrapped keys and salts
- Record and user identifiers
- Operational metadata the server can read
When plaintext appears
When a user reveals, copies, fills, or imports a secret, the plaintext exists in that browser or extension for the moment. Endpoint security, session locking, and the choice of recipient matter for exactly that reason.
- Lock unattended sessions
- Protect the browser endpoint
- Revoke stale paired devices
The cryptography behind it
VaultPilot 3.0.3 uses the browser's Web Crypto API with standard algorithms. The master password never leaves the browser; the server receives only a SHA-256 hash of the key derived from it.
- Master password: PBKDF2-HMAC-SHA-256, 310,000 iterations, 32-byte random salt
- Record values: AES-256-GCM with a random 96-bit nonce for each value
- Vault key: a random AES-256 key wrapped with an RSA-OAEP 3072-bit key pair
- External share packages: PBKDF2-SHA-256 with 420,000 iterations on the passphrase
Limits to know
- Zero knowledge does not protect you from a compromised browser or computer.
- The server can still read operational metadata.
Check step by step
- 01
Keep your master password private; VaultPilot support cannot recover it.
- 02
Confirm the browser supports the required Web Crypto operations.
- 03
Unlock only the vault the authorized task needs.
- 04
When the task ends, lock the session and hide anything you revealed.
Read more in the guides: Security and trust model, VaultPilot overview, Sign-in security screen