
Data boundaries: know what crosses each one before you share
VaultPilot keeps separate data boundaries for browser access, local storage, paired extensions, the optional DC Agent, external packages, update files, and support information.
- Browser to server
- Authenticated requests and encrypted material
- Agent to server
- Directory metadata and health signal
- Support and docs
- Redacted information only
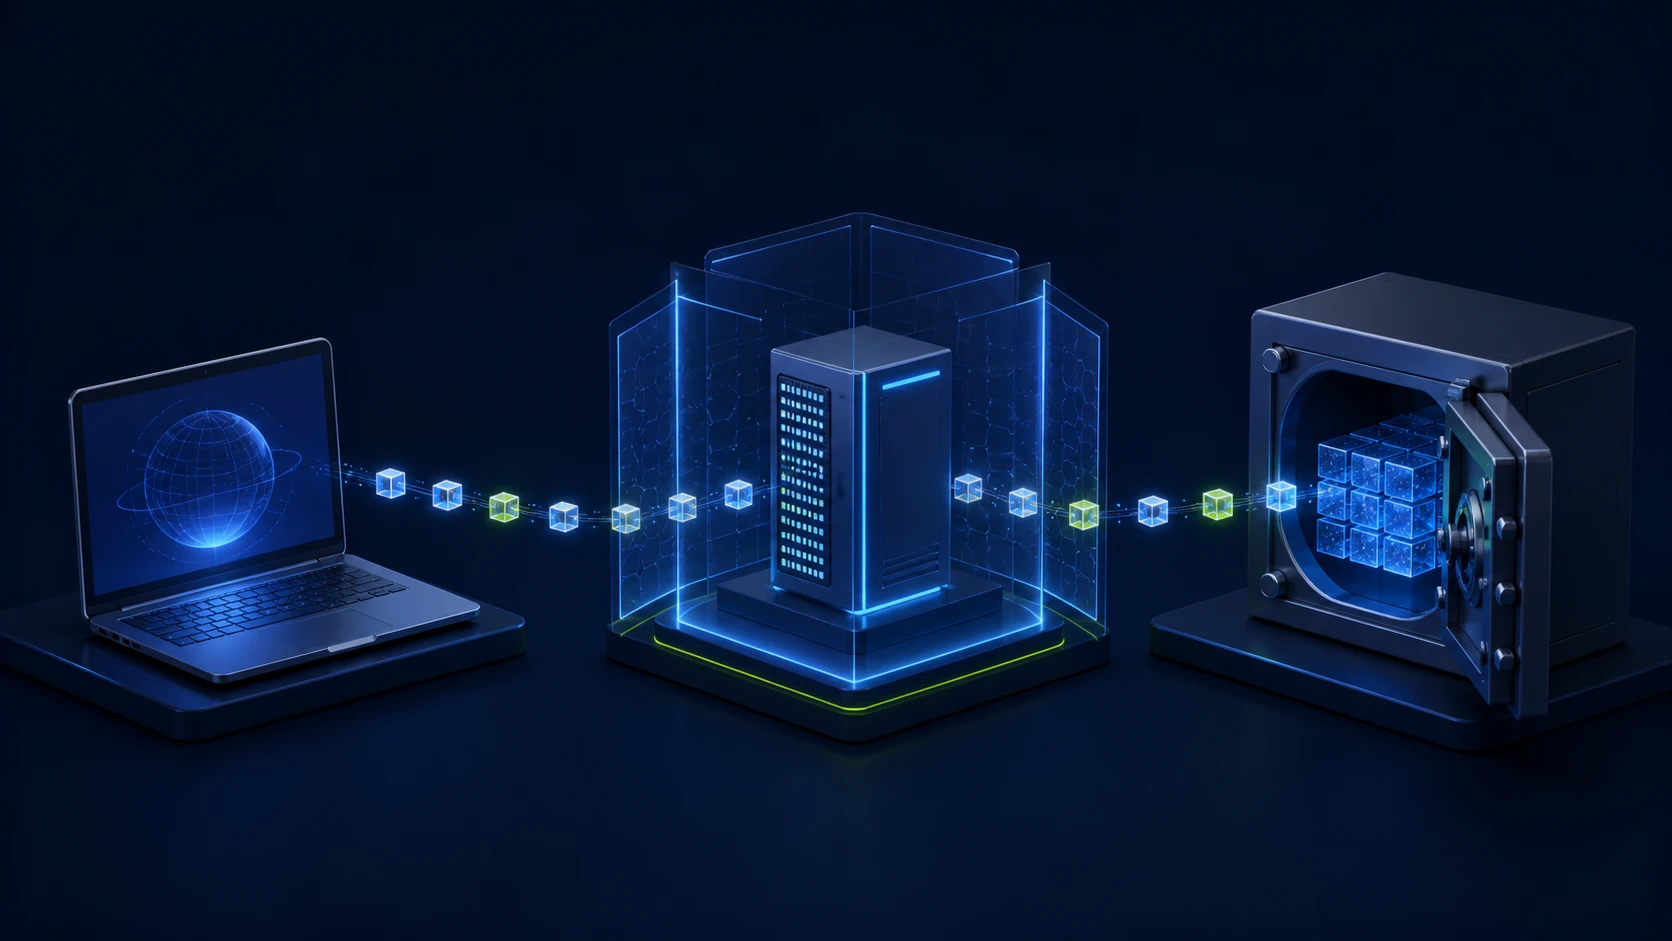
Each component carries different data
The DC Agent never sends the AD bind password; that password stays with the agent setup.
Sharing and updates follow their own paths
External sharing hands an encrypted package of selected records to the recipient's browser. Update Center reads the signed manifest and release assets from the allowed release host before anything is installed.
What may go to support
Version, state, redacted errors, and fictional examples can leave the deployment. Replace real hosts, users, and URLs with placeholders, and remove them from screenshots. A backup file or a raw log goes out only through an approved private channel, and only when that channel asks for it. The items below are never sent.
Limits to know
- Encryption does not make metadata harmless.
- Support email is not a transfer channel for vault exports, databases, or delivery secrets.
- Moving data across a boundary for one task gives no permission to keep or republish it.
Check step by step
- 01
Before a transfer, name the source, destination, purpose, and data class.
- 02
Confirm the receiving component and the operator are authorized.
- 03
Send only the metadata or records the task needs.
- 04
If redaction cannot make the material safe to share, agree on a private path with support first.
Read more in the guides: Security and trust model, Sharing and offline decrypter, Support evidence pack